Services · Compliance
Audit-ready, every quarter.
From gap analysis to certificate — and the evidence ledger that keeps you compliant after the auditor leaves.
- 6+Major standards covered
- GDPRDPO-as-a-service available
- PCIAll DSS levels supported
- 12+Years in compliance
Compliance, assessed and maintained
We take you from gap analysis to certification — and keep you compliant as regulations evolve.
Regulations like GDPR, PCI-DSS, ISO 27001, e-KYC/AML, and NIS2 carry real penalties and real complexity. We translate them into a practical program tailored to your industry, data, and risk.
Our specialists assess where you stand, close the gaps, and embed the policies and controls that keep you compliant — then stand beside you through audits and ongoing monitoring.
Six frameworks, stamped when they pass
Each seal stamps as it comes into view; beneath it, what the framework demands and how we evidence it.
GDPR
European UnionThe EU's data-protection law: how personal data may be collected, used, shared and kept, and what the people it describes can demand of you.
- Lawful basis for every processing activity
- Record of processing activities (Art. 30)
- Data-subject rights within one month
- Privacy by design and by default (Art. 25)
- 72-hour breach notification (Arts. 33–34)
e-KYC / AML
Moldova · Romania · EURemote customer identification and anti-money-laundering controls for banks, non-bank lenders and fintechs — National Bank of Moldova rules under Law 308/2017, National Bank of Romania rules under Law 129/2019, and the EU AML framework they both transpose.
- Customer identification and verification
- Risk-based customer due diligence
- Sanctions, PEP and adverse-media screening
- Beneficial ownership
- Record keeping — five years
PCI DSS
GlobalThe card brands' security standard for anyone who stores, processes or transmits cardholder data — twelve requirements, validated every year.
- Secure network and systems (Req. 1–2)
- Protect stored account data (Req. 3)
- Encrypt in transit (Req. 4)
- Access control and identity (Req. 7–8)
- Logging, monitoring and testing (Req. 10–11)
ISO 27001 / 27701
GlobalThe international standard for an information-security management system, and its privacy extension — the certificate enterprise customers ask for first.
- Context, scope and leadership (Clauses 4–5)
- Risk assessment and treatment (Clause 6)
- Organisational controls (A.5)
- Technological controls (A.8)
- Performance evaluation and improvement (Clauses 9–10)
SOC 2 Type II
GlobalAn independent auditor's report on how your security, availability, confidentiality, processing-integrity and privacy controls operated over a period — the report US enterprise buyers ask for.
- Common Criteria — Security (CC1–CC9)
- Logical and physical access (CC6)
- System operations and incident response (CC7)
- Change management (CC8)
- Availability criteria (A1)
NIS2
European UnionThe EU's cybersecurity directive for essential and important entities — mandatory risk-management measures, tight incident reporting and personal accountability for management.
- Risk analysis and security policies
- Incident handling
- Supply-chain security
- Business continuity and crisis management
- Incident reporting — 24 h / 72 h / 1 month
Four stages, repeated — not run once.
Regulations evolve; so does the programme. A pulse runs the ring: where you are in the cycle at any moment.
- 01
Assess
We run a gap analysis against the relevant standards to show exactly where you stand.
- 02
Plan
We prioritize remediation and design policies and controls tailored to your industry and data.
- 03
Implement
We put the controls, documentation, and processes in place and prepare your evidence.
- 04
Certify & maintain
We support the audit and provide ongoing monitoring so you stay compliant over time.
Capabilities
GDPR & Data Protection
Full adaptation and compliance of internal company programs and processes to EU General Data Protection Regulation 2016/679. Data protection impact assessments, privacy by design implementation, DPO-as-a-service, and breach notification procedures.
PCI-DSS Compliance
Payment Card Industry Data Security Standard compliance for organizations handling cardholder data. Gap analysis, remediation planning, SAQ assistance, and ongoing compliance monitoring for all PCI-DSS levels.
ISO & SOC Certifications
Consultancy and support for ISO 27001 (Information Security), ISO 9001 (Quality), ISO 22301 (Business Continuity), SOC 2 Type I/II audits, and NIS2 directive compliance for critical infrastructure operators.
e-KYC & AML Compliance
Electronic Know Your Customer programmes for banks, non-bank lenders and fintechs: remote identity verification with document and liveness checks, customer due diligence and risk scoring, sanctions and PEP screening, transaction monitoring and audit-ready record keeping — built for Moldova (National Bank of Moldova, Law 308/2017), Romania (National Bank of Romania, Law 129/2019) and the wider EU AML framework. We integrated a rigorous e-KYC flow of this kind for eCredit's digital lending platform.
The numbers we stand behind.
The figures behind every engagement, and the frameworks each one maps to.
Built for teams like yours
Industries
Use cases
- Achieve PCI-DSS or ISO 27001 certification
- Become GDPR or e-KYC/AML compliant
- Outsource the Data Protection Officer function
- Stay audit-ready all year round
Why run compliance with KYAX
Less audit stress, fewer surprises, lasting compliance.
Tailored programs
Compliance mapped to your industry, data, and risk — never a generic checklist.
Security-backed
Our in-house security team implements the technical controls behind every standard.
Audit support
We prepare the evidence and stand with you through certification audits.
Stay compliant
Ongoing monitoring and DPO-as-a-service keep you compliant as rules and your business change.
Our Commitment
Four commitments that outlast any single audit.
Data Protection
Your data is protected with industry-leading security measures
Transparency
Clear communication about our compliance practices
Continuous Improvement
Regular updates to meet evolving regulatory requirements
Expert Support
Dedicated compliance team to address your concerns
Outcomes we've delivered
Real numbers from real client projects.
Selected work
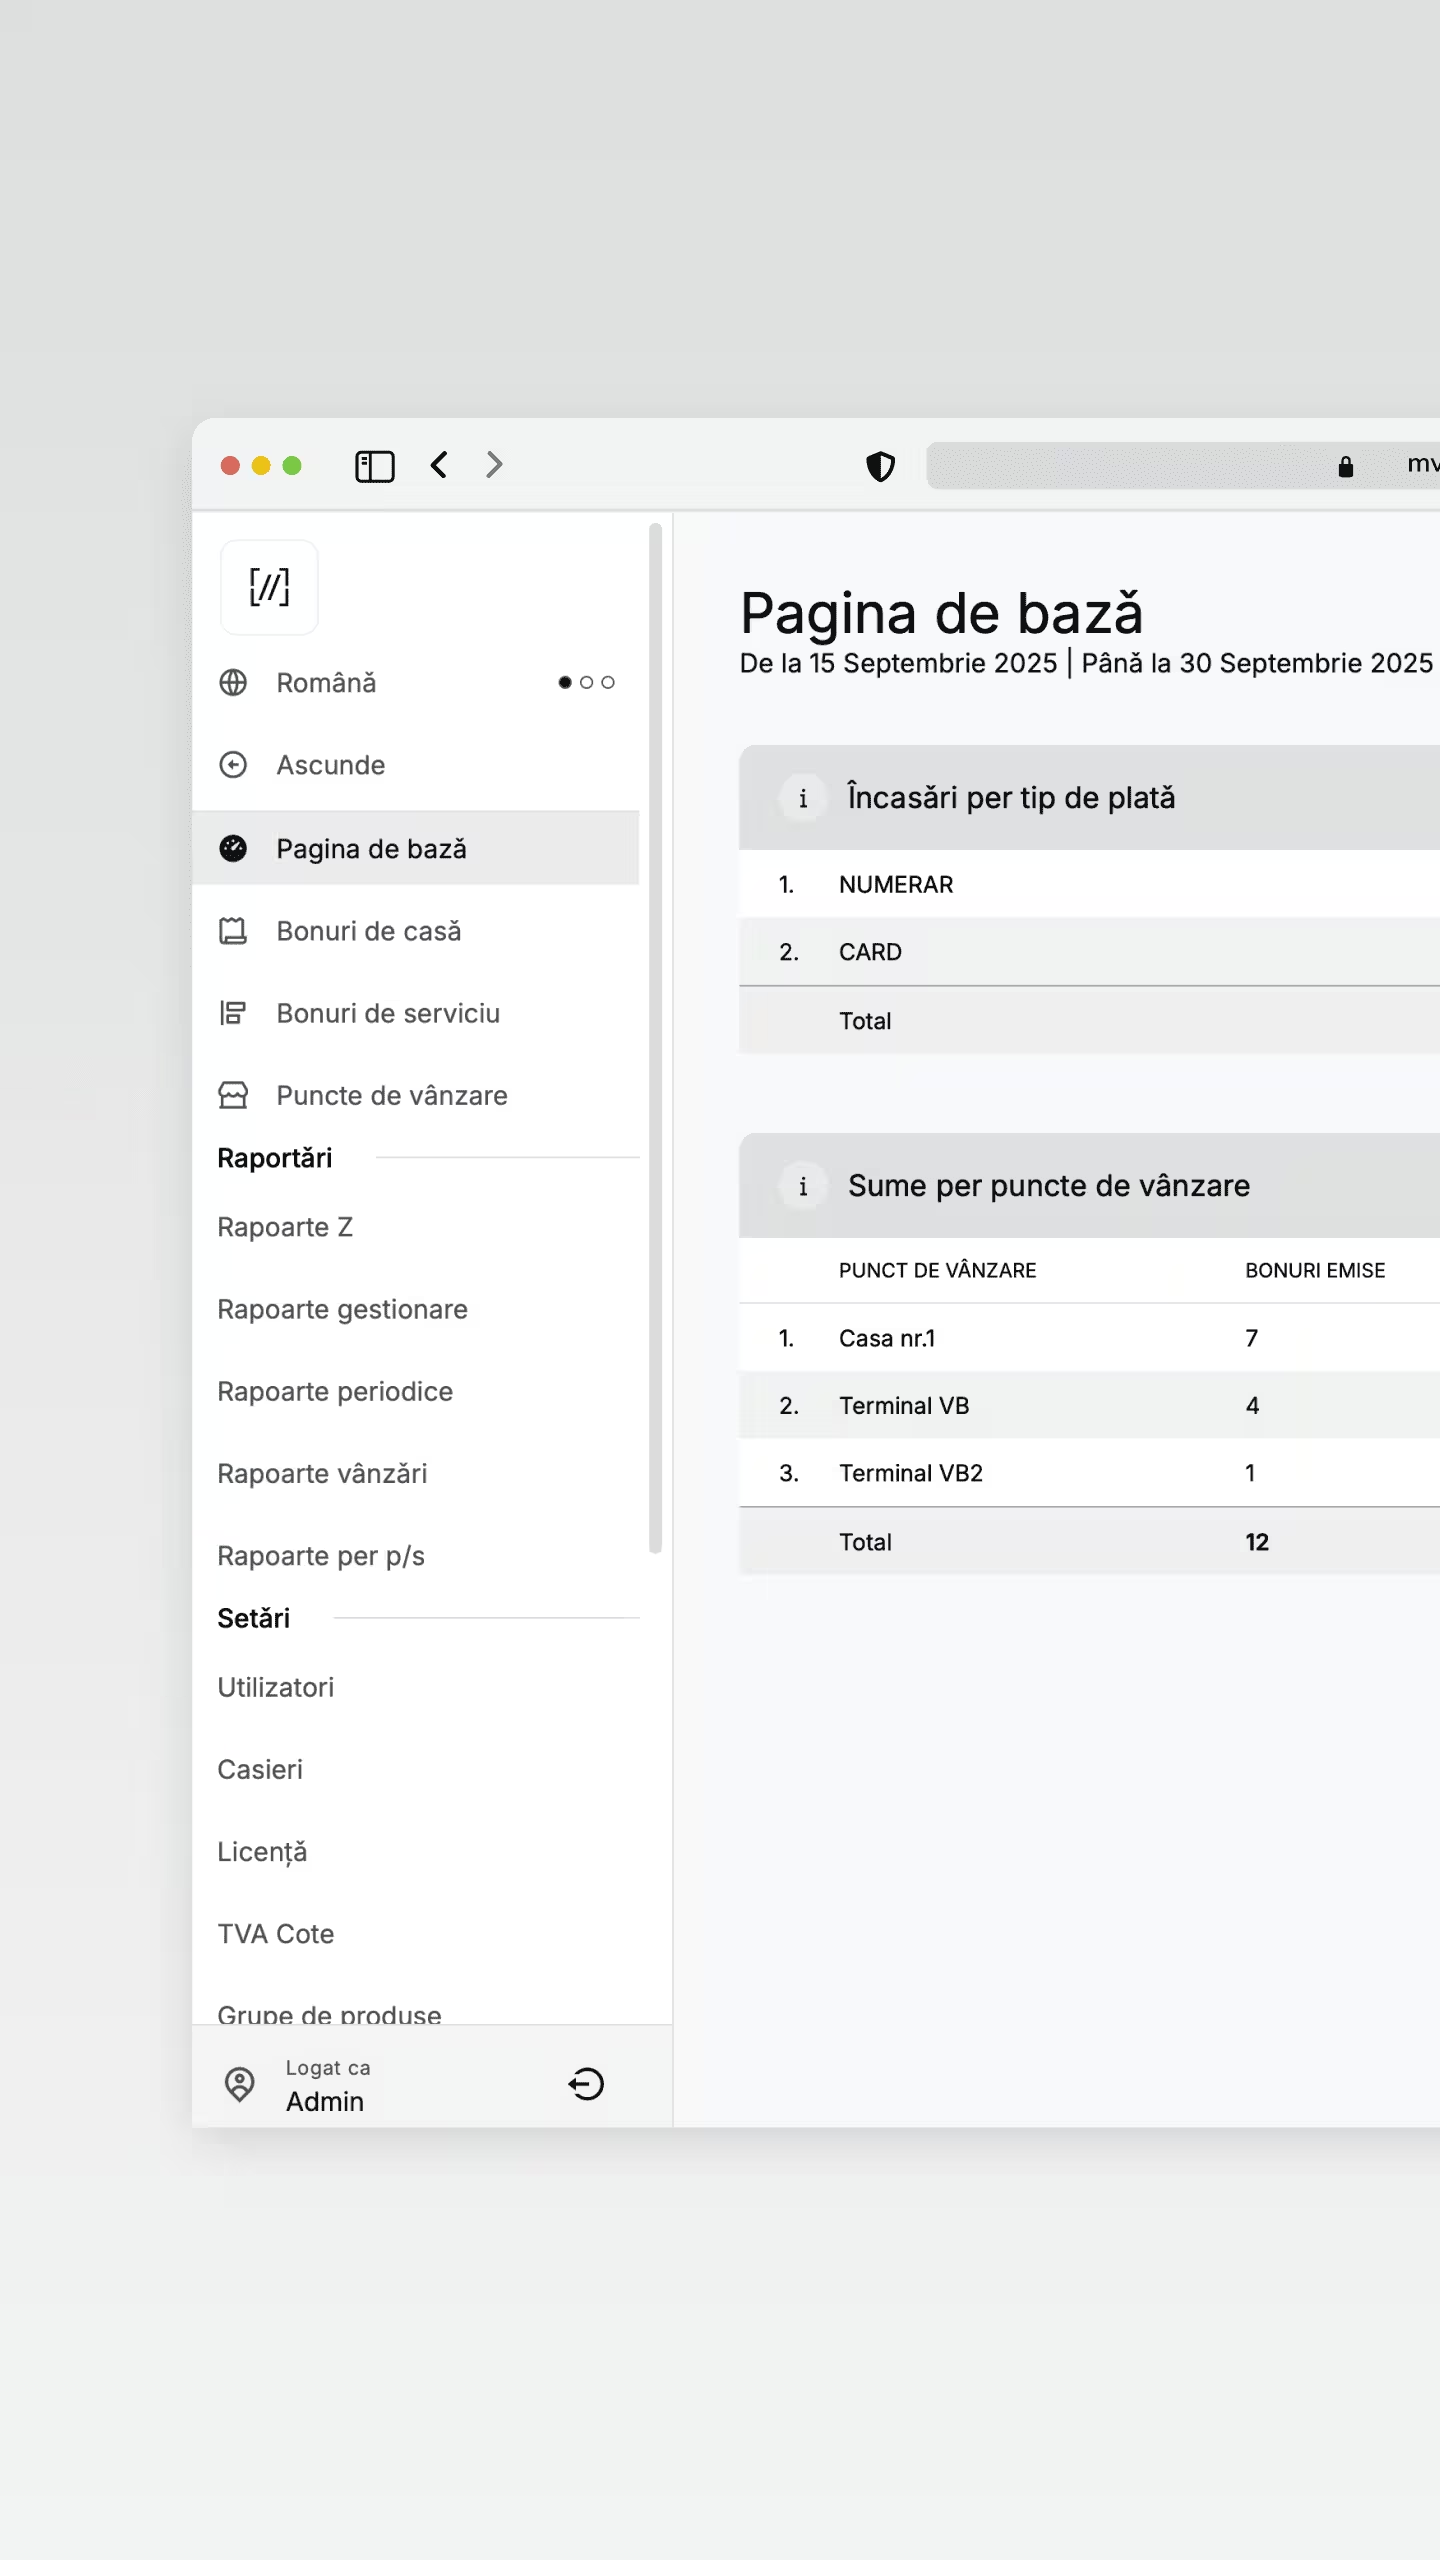
A few projects where we put this expertise to work.
Compliance questions, answered
Which standard do we actually need?
It depends on your industry, location, and the data you handle — for example PCI-DSS for card payments, e-KYC/AML for lenders and fintechs, GDPR for EU personal data. We start by identifying exactly which obligations apply to you.
How long does it take to become compliant?
It varies with scope and your starting point, which is why we begin with a gap analysis. That gives you a realistic, prioritized timeline rather than a guess.
What is DPO-as-a-service?
We act as your outsourced Data Protection Officer — overseeing GDPR compliance, handling data-protection questions, and managing breach-notification procedures — without the cost of a full-time hire.
Can you maintain our compliance, not just set it up?
Yes. Compliance isn't one-and-done. We provide ongoing monitoring, reviews, and updates so you stay compliant as standards and your business evolve.
Other services
Ready to Transform Your Business?
Let's discuss how our expertise in IT security, development, and DevOps can help you achieve your goals.